
Needl.ai cloud
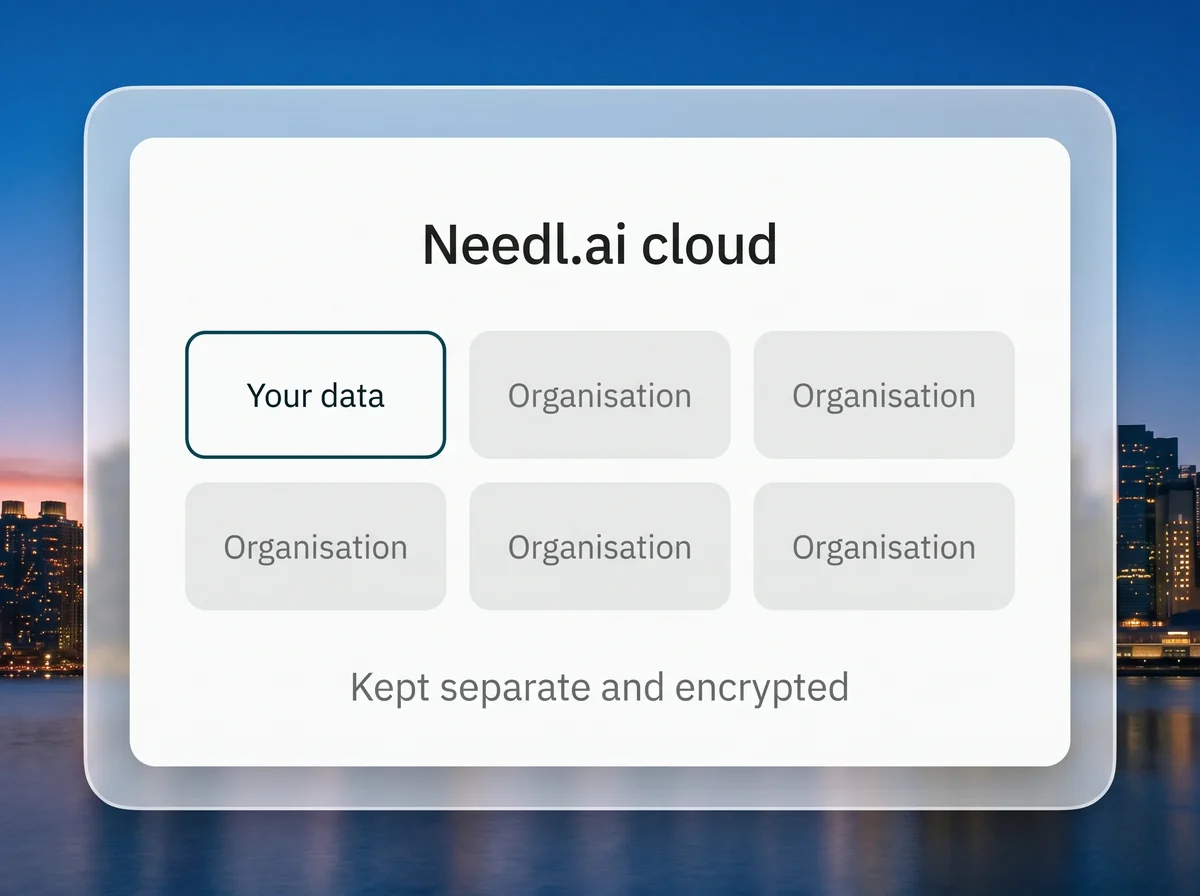
Our managed cloud. Each organisation's data is kept separate, encrypted and access-controlled under our SOC 2 Type II and ISO 27001 controls.
- Runs in
- Needl.ai's managed cloud
- Operated by
- Needl.ai
- Best for
- Trials and fast starts
Needl.ai runs in your own cloud account, on premise, or in a dedicated instance we operate for you. It follows your permissions, never trains on your data, and is independently audited for SOC 2 Type II and certified to ISO 27001.
The same commitments apply in every deployment.
Your documents, questions and outputs are never used to train any model, ours or a model provider's.
Data is encrypted in transit with TLS 1.2 or higher and at rest with managed keys. Credentials for your connected systems are encrypted with AES-256.
Each finding links to the page it came from, so a reviewer can open the source and check it.
Questions, answers and the sources behind them are kept on record. In your own cloud, infrastructure activity lands in your own logs.
Ask us and we delete your documents, indexes and everything derived from them, then confirm it in writing.
Sign in with your Microsoft account, so access follows your identity provider.
Three ways to run Needl.ai, each with the same security controls. Start in our cloud and move into your own environment when you are ready.
Our managed cloud. Each organisation's data is kept separate, encrypted and access-controlled under our SOC 2 Type II and ISO 27001 controls.
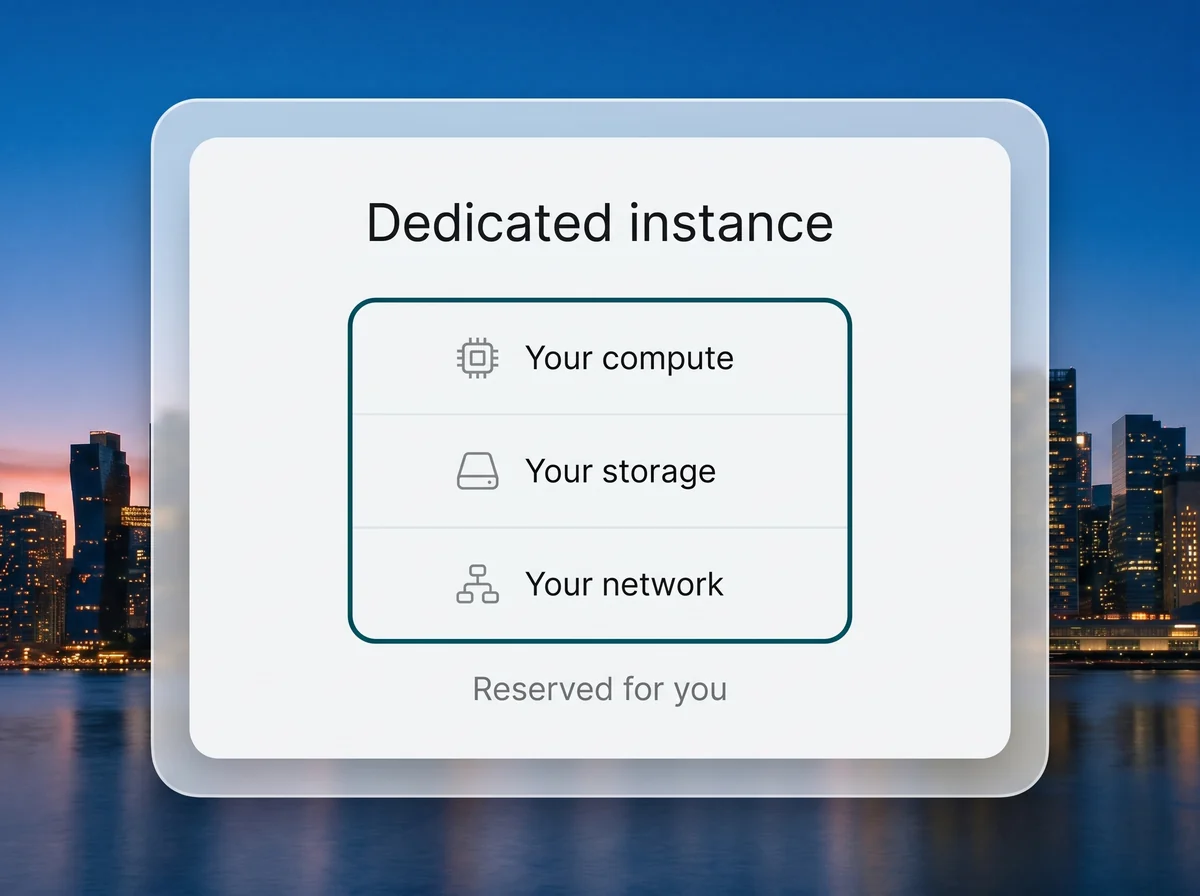
A single-tenant deployment reserved for you, with its own infrastructure and no compute or storage shared with anyone else. We operate it for you.
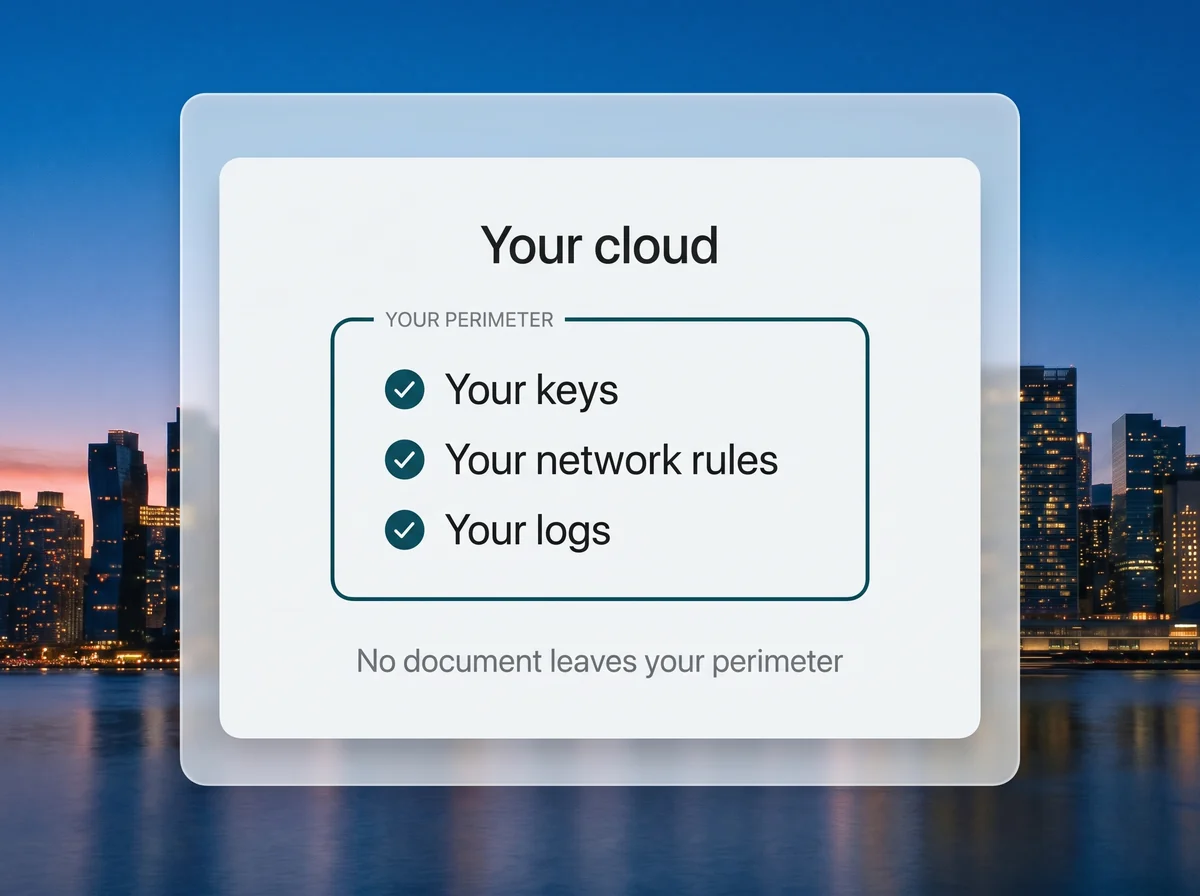
Installed in your own AWS or Azure account, or on your own servers. Your keys, your network rules and your logs. No document leaves your perimeter.
Security sits in the product as well as the infrastructure. Three safeguards are part of the platform itself.
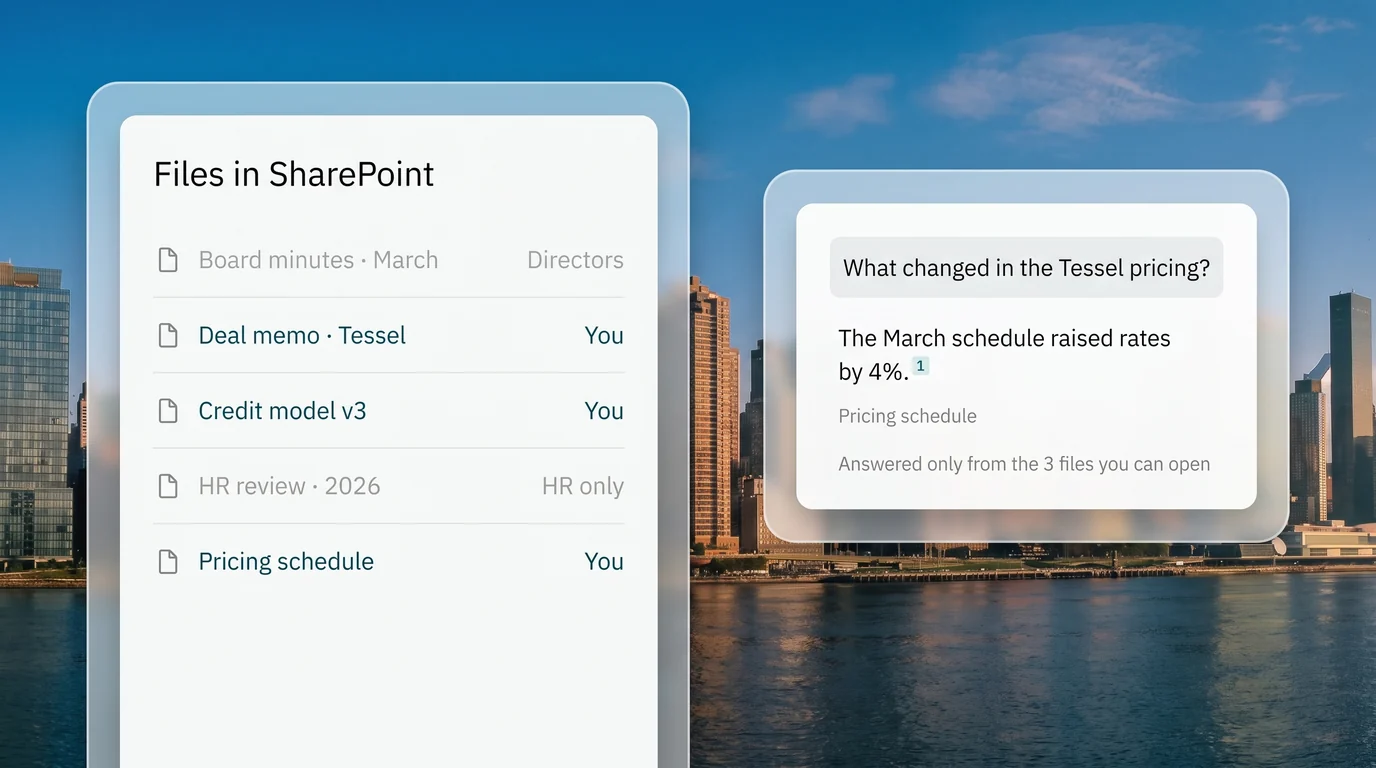
Needl.ai reads each document with the access every person has in the source system and records who can open it. Every search and answer is filtered by that record, so people only get results from files they could already open.
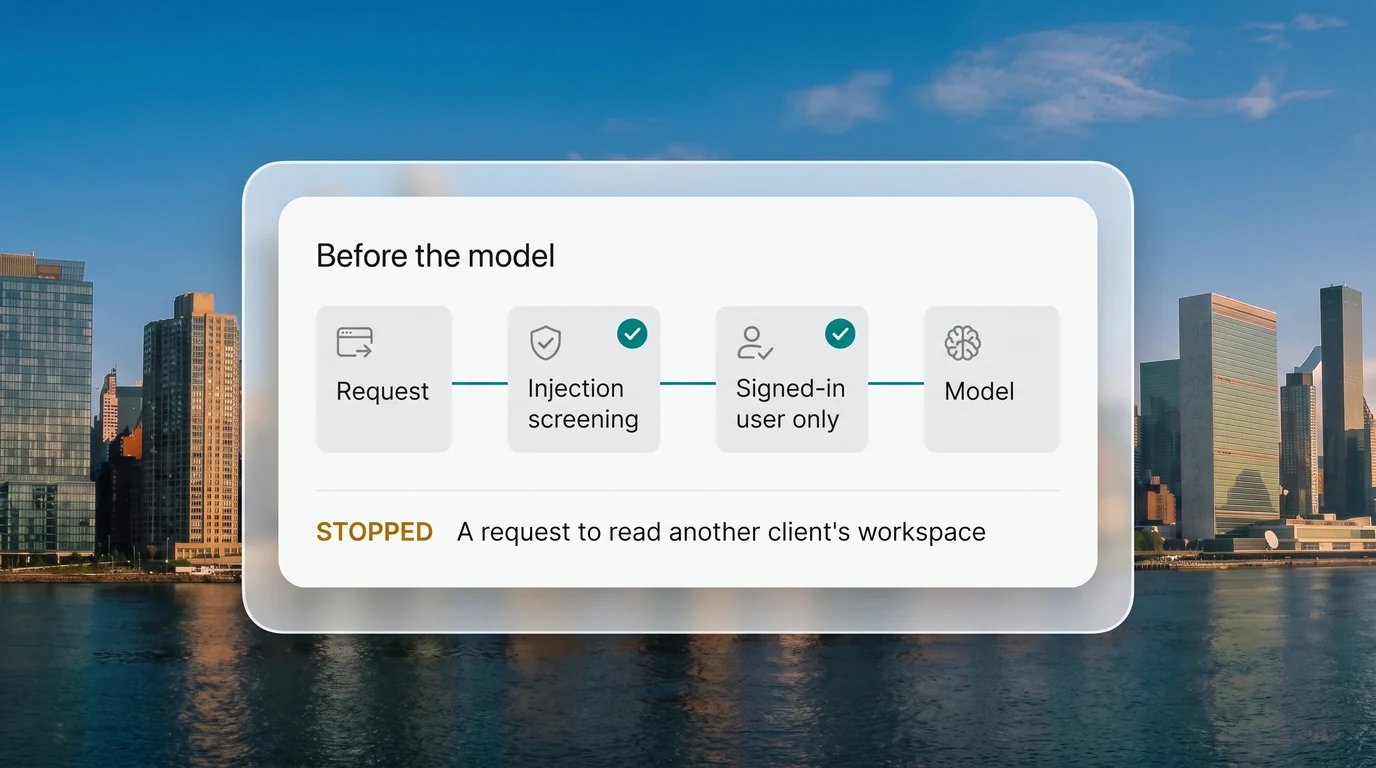
A guardrails service sits in front of the language model, and each application switches on the checks it needs. A dedicated detection model screens prompts for injection attempts. What an assistant can reach is fixed by who is signed in, so a prompt cannot change it, and attempts to switch to another client's context are rejected.
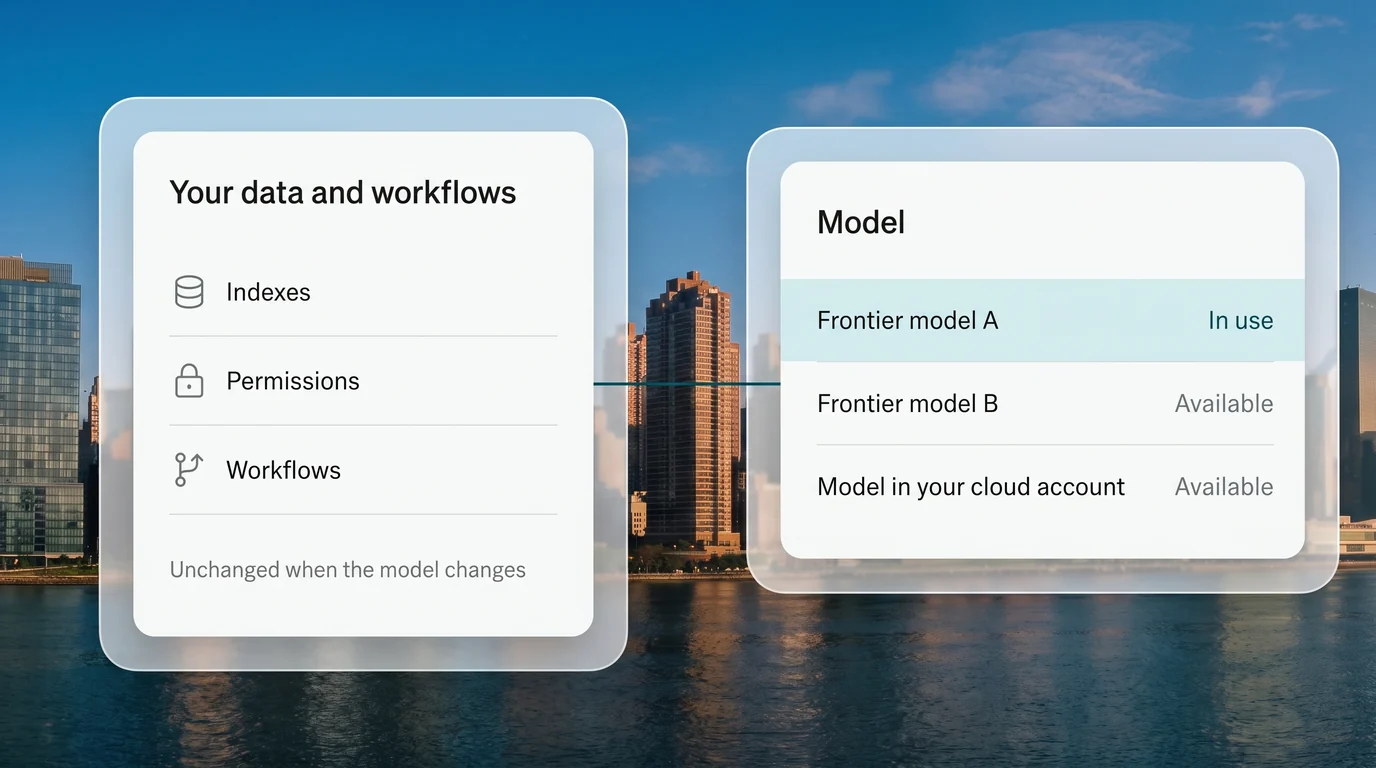
Needl.ai keeps your data and workflows separate from the model underneath. Run on the model your firm has approved, including models hosted in your own cloud account. If a provider changes its terms or access, we switch models with no change to your data or workflows.
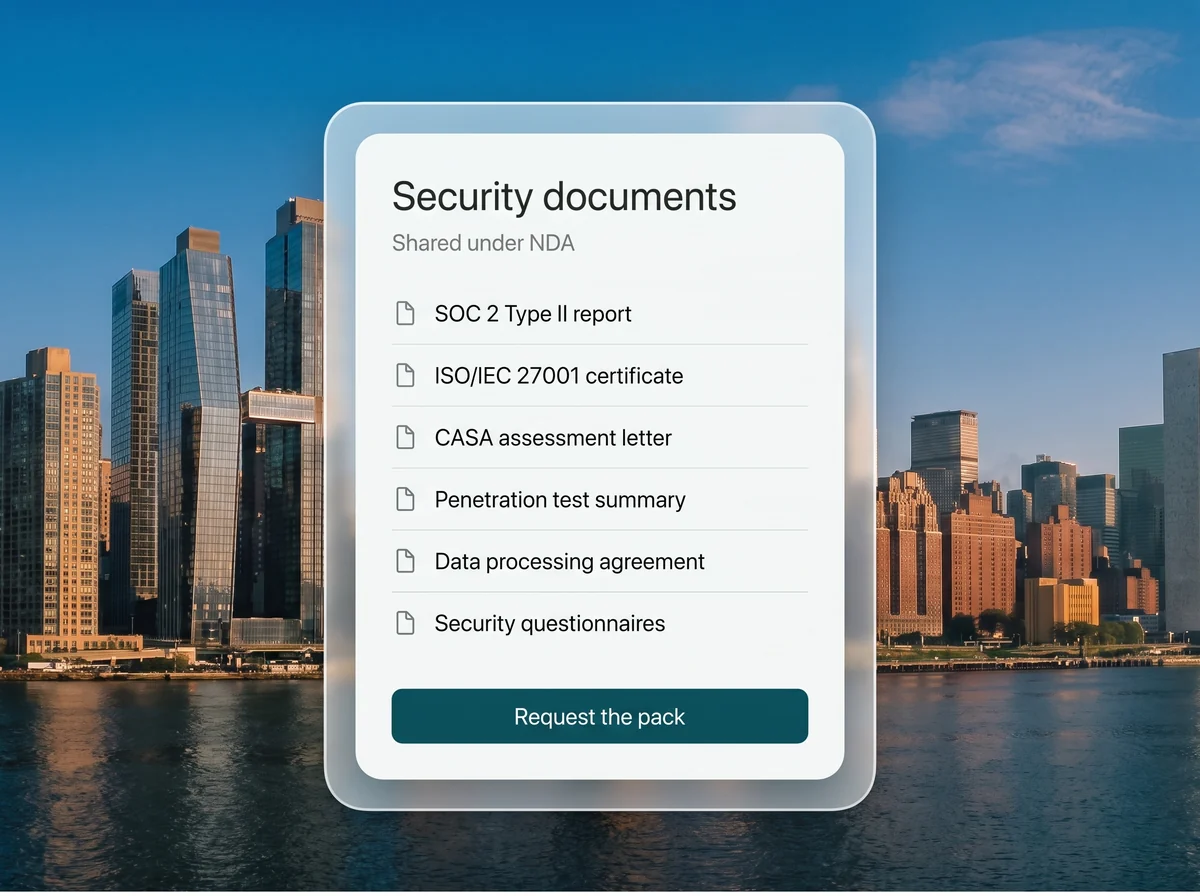
Our controls are tested by independent auditors, and the reports are available under NDA.
An independent audit of how our security controls operate over time. Report available under NDA.
A certified information security management system, with annual surveillance audits.
Google's Cloud Application Security Assessment, for the connectors that read Gmail and Google Drive.
Personal data handled in line with the GDPR, with a data processing agreement available on request.
Independent vulnerability assessment and penetration testing. Summary available under NDA.
The international standard for AI management systems. Our certification audit is in progress.
“Needl.ai gave us enterprise-grade assurance, no compliance risks, no shadow AI, and complete control over our data environment.”
What security and risk teams ask before approving Needl.ai.
Where you choose: in your own AWS or Azure account or on premise, in a dedicated instance reserved for you, or in the Needl.ai cloud. You can start in our cloud and move into your own environment later.
No. Your documents, questions and outputs are never used to train any model, ours or a model provider's.
Needl.ai works with the leading frontier models and can run on the model your firm has approved, including models hosted in your own cloud account. Your data and workflows stay separate from the model, so a switch needs no change on your side.
In your own cloud or on premise, only the people you grant access. In a dedicated instance or the Needl.ai cloud, access is limited to authorised Needl.ai staff who need it to run the service, under the controls audited for SOC 2 Type II and ISO 27001.
Needl.ai records who can open each document in the source system and filters every search and answer by that record. People only get results from files they could already open. The context infrastructure note explains how.
Yes. Ask us and we delete your documents, indexes and everything derived from them, then confirm it in writing.
Yes. We sign a mutual NDA before any data is shared, and provide a data processing agreement for your review.
Yes. Our SOC 2 Type II report, ISO 27001 certificate, CASA letter and penetration test summary are available under NDA.
One request covers the full pack. We share it under NDA and can walk your risk and compliance teams through the details.